Releases with health checks
Approve a product once. Each new release moves through your rings and advances only when boot checks, event logs and your own health signals pass, right away or on your schedule.
Automation Workflows

Endpoint management for Windows, Linux and macOS
Patchblox adds what Intune and Azure Update Manager leave out: release rings with health checks for Windows, Linux and third-party apps, security baselines scored with evidence from each device, the full version history of your Intune policies, and real-time actions on any endpoint. Run it in your own environment.
Private Hosted ships in Q1 2027.
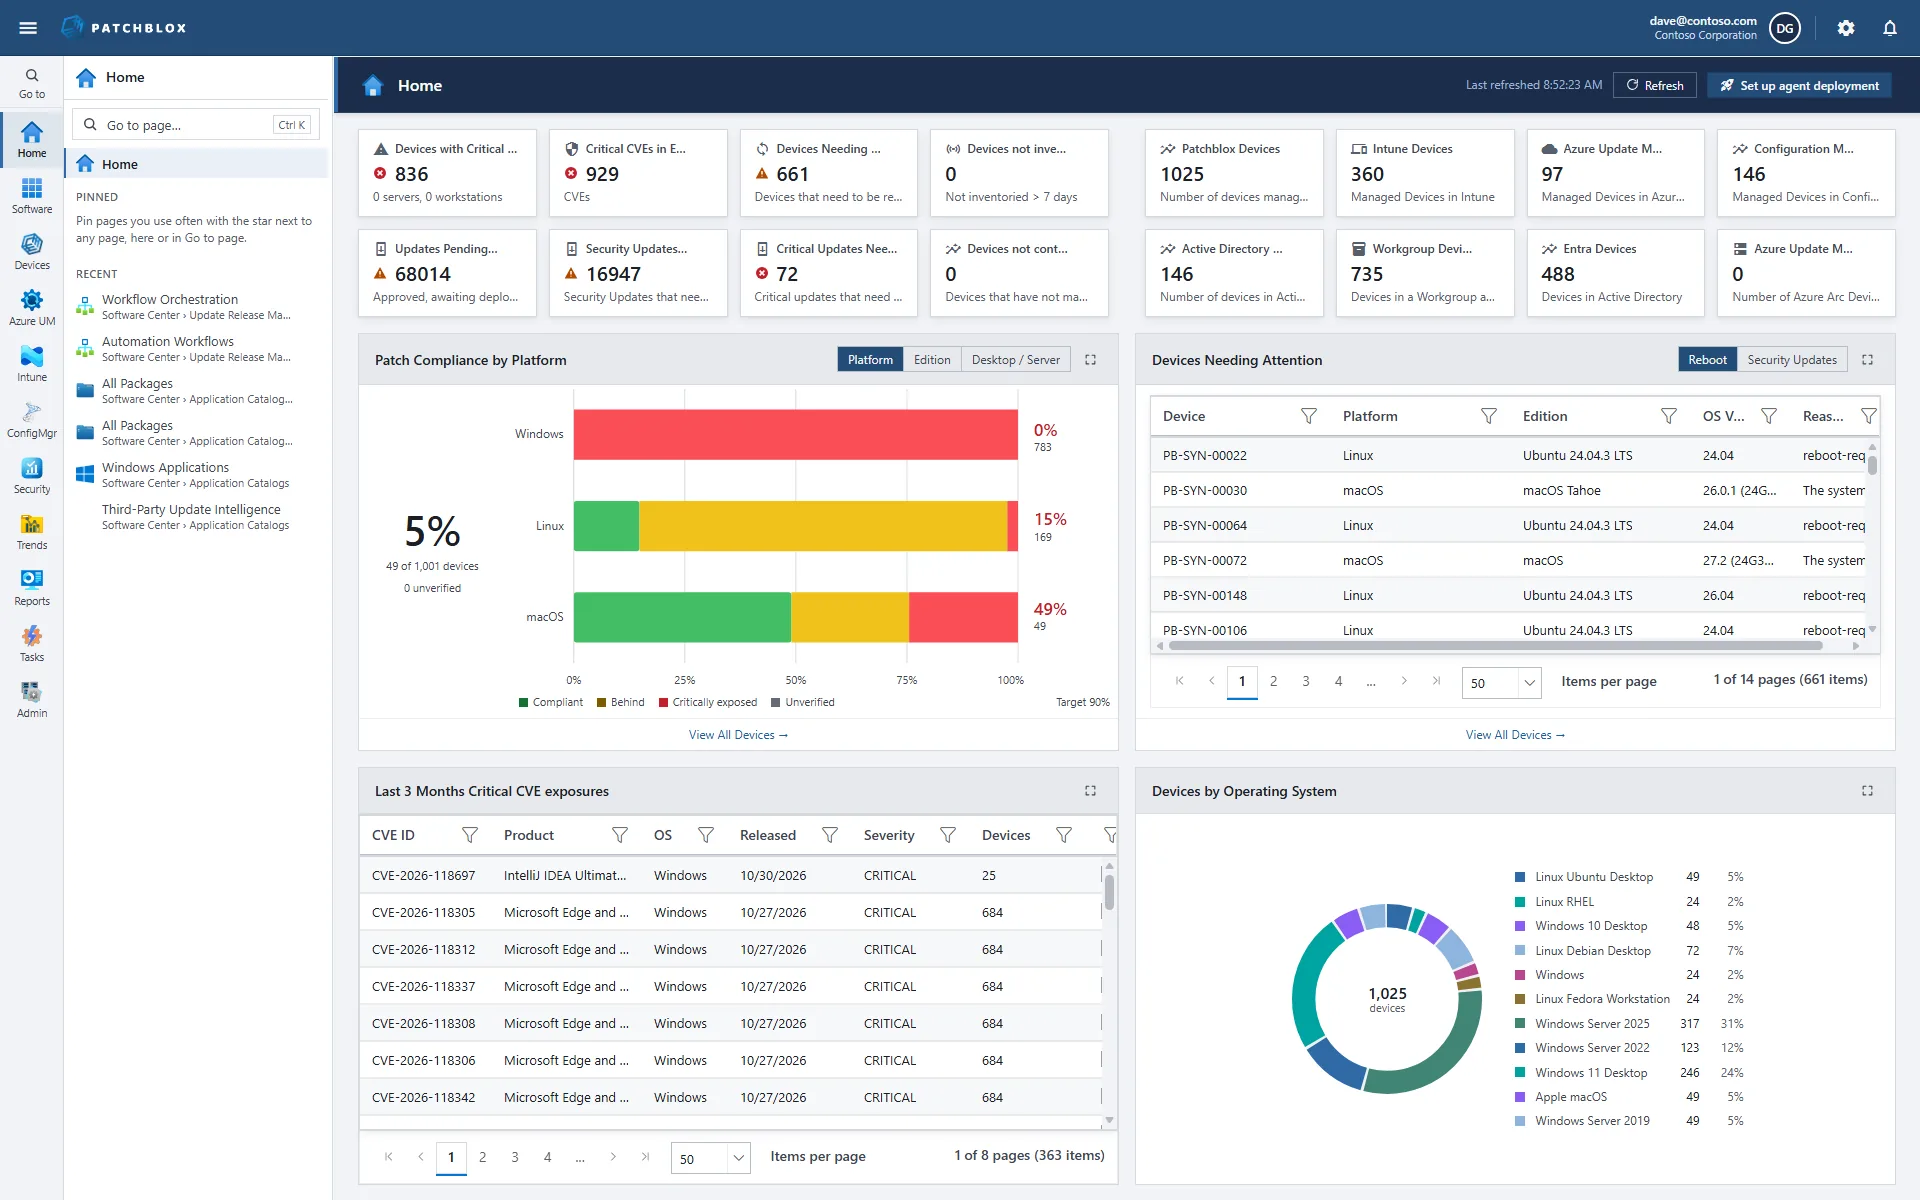
Approve a product once. Each new release moves through your rings and advances only when boot checks, event logs and your own health signals pass, right away or on your schedule.
Automation WorkflowsScore devices against Industry Standard, DISA STIG and Microsoft SCT baselines, and see the actual value behind every failed rule.
PostureEvery policy version kept and compared, drift from your approved version flagged, and any version restored under your own sign-in.
GovernanceHundreds of actions with a live result from each device, over an outbound connection that needs no inbound ports.
OperationsAn endpoint platform can change every device you own, so it has to be hard to misuse.
A certificate authority for each customer. You keep the root key offline.
Every script and task is signed, and the agent verifies it before it runs.
Agents connect out to their gateway. Nothing listens on your endpoints.
Changes in Intune and Azure use your admin's own delegated sign-in.
Private Hosted runs entirely in your environment.
Built by a team with 30+ years in endpoint management, including BindView and EminentWare. How Patchblox is built | About us
Every security fix for Microsoft, Windows apps, macOS and Linux, ranked by whether attackers are using it. Free, updated several times a day.
| Fix | Applies to | Why | Priority |
|---|---|---|---|
| Google Chrome 156.0.8078.80 | Google Chrome | Closes CVE-2026-2441, exploited (CISA KEV), plus 203 more | Patch now |
| RHSA-2026:87080 | apcu-panel, libzip, libzip-devel and 34 more on RHEL 8 | Closes CVE-2026-109618, exploited (CISA KEV), plus 11 more | Patch now |
| Google Chrome Beta 158.0.8127.2 | Google Chrome Beta | Closes CVE-2026-2441, exploited (CISA KEV), plus 200 more | Patch now |
The most urgent fixes released recently, one per operating system where there is one.
From the blog, by Dave Gayler
Autonomy is easy to demo. Containment isn't. Twenty questions to ask your endpoint management, network management and monitoring vendors before you turn it on.
Read the articleA walkthrough of Automation Workflows, baselines and Intune governance on a realistic demo tenant, with time for your questions.